Security Practices & Source Ownership
Designed to support client security requirements, data privacy, and full software ownership.
Security Engineering Practices
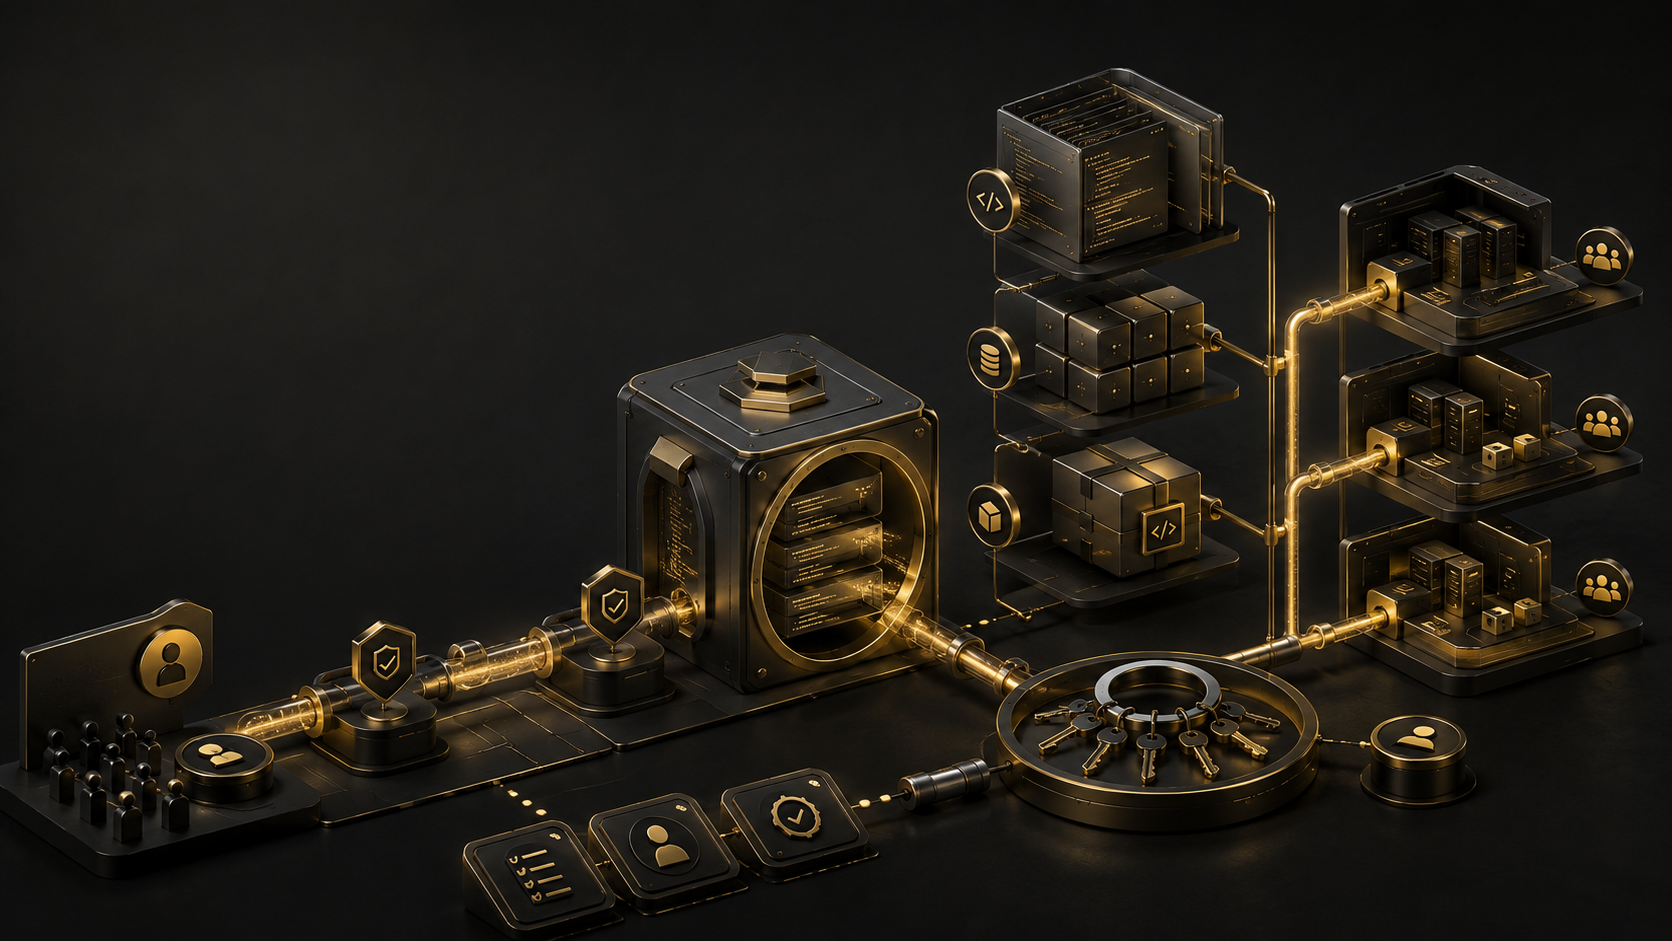
Least-Privilege Access
Development access is strictly granted on a least-privilege, role-isolated basis. Client staging and production environments are strictly separated.
Secret & Credentials Management
No hardcoded API keys or credentials in source code. Credentials are managed via secure vault integrations and transferred through encrypted channels.
Encrypted Transport & Storage
All network data transport utilizes TLS 1.3 encryption. Database backups and sensitive columns support at-rest encryption standards.
Dependency & Code Scanning
Automated dependency vulnerability scanning (GitHub Dependabot/Snyk) is enforced across all engineering repositories.
What You Receive & Own
Upon completion of each fixed-price milestone and cleared payment, full ownership is transferred directly to your organization:
- Source Code: Complete Git repository with clear commit history and standard build scripts.
- Database Schemas: Entity definitions, migration scripts, and seed/configuration scripts.
- Deployment Materials: Dockerfiles, CI/CD pipeline definitions, and environment configuration templates.
- Access Revocation: Formal revocation of Brass Tracks credentials from client infrastructure following handover.
Before a project begins
Bring your actual security and handoff requirements.
We can scope access boundaries, environments, ownership, deployment responsibilities, and handoff materials into the delivery plan. Requirements are discussed against the actual project—not presented as generic guarantees.